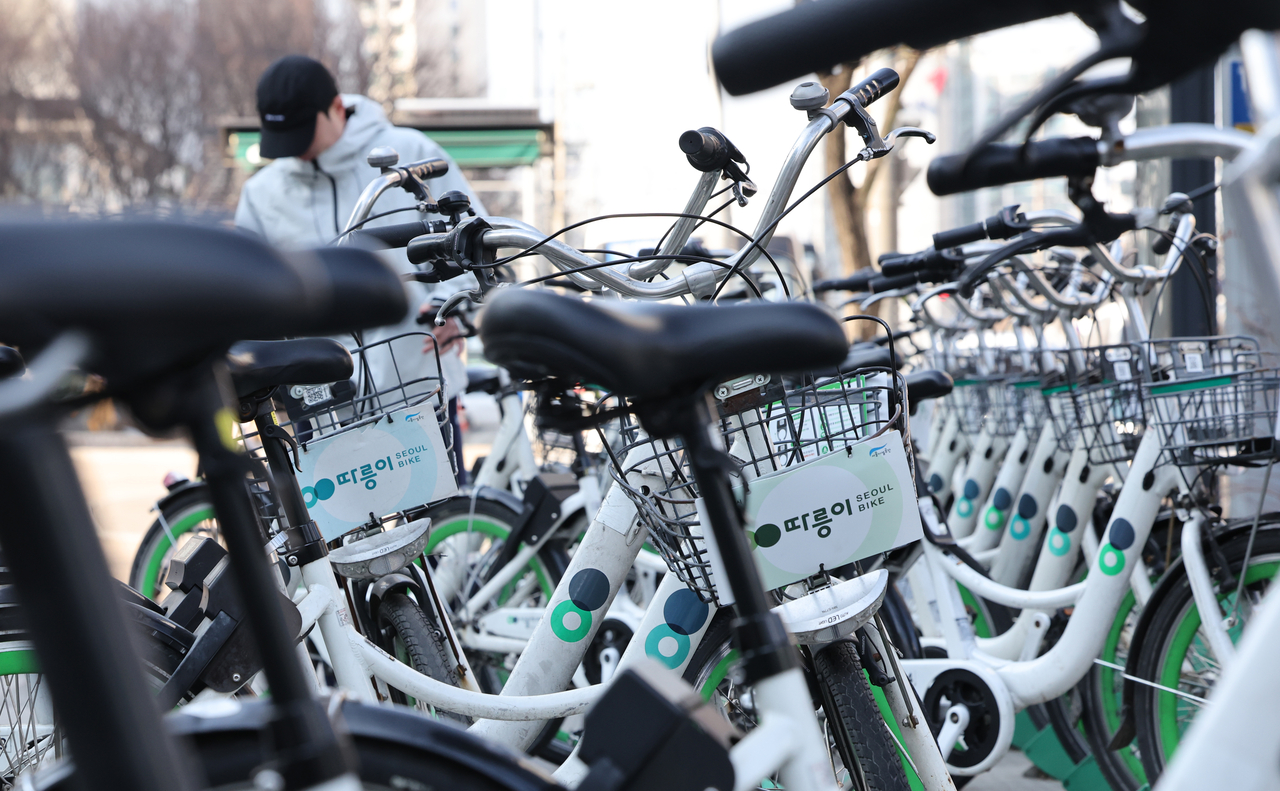
Two teenagers were found to be behind the leak of personal information belonging to 4.62 million users of Seoul’s public bike-sharing service “Ttareungi”, police said Monday.
The Seoul Metropolitan Police Agency’s cybercrime investigation unit said it had apprehended two high school students on charges of violating the Information and Communications Network Act. The suspects were forwarded to prosecutors without detention.
The data breach occurred between June 28 and 29, 2024, involving 4.62 million registered accounts on the Ttareungi app operated by the Seoul Facilities Corporation. The leaked information included user IDs, mobile phone numbers, email addresses, home addresses, dates of birth, gender and body weight. Authorities clarified that unique identification information, such as names and resident registration numbers, was not included, and no signs of secondary damage or misuse have been detected so far.
The case was uncovered during a separate cybercrime investigation. Police said they identified signs of the Ttareungi data leak while probing a distributed denial-of-service attack carried out in April 2024 against a private shared mobility company.
During forensic analysis of electronic devices seized from one of the suspects in the DDoS attack, investigators discovered files containing Ttareungi users’ personal data. Police later arrested another suspect, who allegedly conspired in the breach.
Investigators said structural vulnerabilities in the app’s authentication system enabled the teenagers to access and extract the data within two days. The Ttareungi app reportedly had a security flaw that allowed user information to be accessed without proper authentication.
According to police, the two suspects met through Telegram and conspired to commit the crime while studying information security independently. After identifying vulnerabilities in the Seoul Facilities Corporation’s server, one suspect informed the other, who allegedly proposed extracting the entire personal data file from the Ttareungi server.
One suspect told police he committed the crime out of “curiosity and a desire to show off,” while the other has exercised his right to remain silent. Prosecutors rejected police requests for arrest warrants for the former twice, citing his status as a juvenile.
Meanwhile, police have launched a preliminary inquiry into officials at the Seoul Facilities Corporation for allegedly failing to take action for nearly two years despite being aware of the data breach.
The Seoul Metropolitan Government said in a briefing on Feb. 6 that the corporation had confirmed the leak following a cyberattack in June 2024 but did not take appropriate measures, and requested a police investigation on suspicion of violating the Personal Information Protection Act.
Police added that all suspects have been apprehended and their electronic devices seized.
“We will work closely with the Personal Information Protection Commission to prevent a recurrence and minimize potential secondary damage,” an official said, urging the public to exercise caution against suspicious messages or financial transaction requests from unknown sources.
ylee221@heraldcorp.com