A critical security flaw in Java, discovered weeks after vulnerabilities in PHP, has prompted South Korea to urge immediate security checks and convene an emergency cybersecurity meeting involving government, industry and military officials.
The Ministry of Science and ICT and the Korea Internet and Security Agency warned Wednesday that vulnerabilities in OpenJDK, a widely used Java platform, could allow attackers to remotely execute malicious code without authentication under certain conditions.
One of the flaws, dubbed Java4Shell (CVE-2026-114938), stems from a memory corruption bug in OpenJDK's Base64 decoder. Exploiting the vulnerability requires specific hardware and software conditions.
Java is widely used in corporate and government IT systems, including web services, groupware and enterprise resource planning software, raising concerns about potential risks to critical operations.
Oracle released patches Tuesday (US time), addressing 11 vulnerabilities in Java SE, including flaws affecting certain versions of Java SE and GraalVM.
The ministry and KISA urged organizations to check their Java installations and apply the latest security updates, prioritizing internet-facing services and critical business systems. They also advised administrators to verify that the patches had been properly applied.
Cheong Wa Dae said Wednesday that its national security office had convened an emergency meeting the previous day after obtaining information about the Java vulnerabilities ahead of their public disclosure.
The meeting brought together senior officials from the science, defense and interior ministries, the National Intelligence Service and financial regulators to review Java usage and security measures across the public, private and defense sectors.
Participants agreed to share threat intelligence and updates on security measures in real time to coordinate their response.
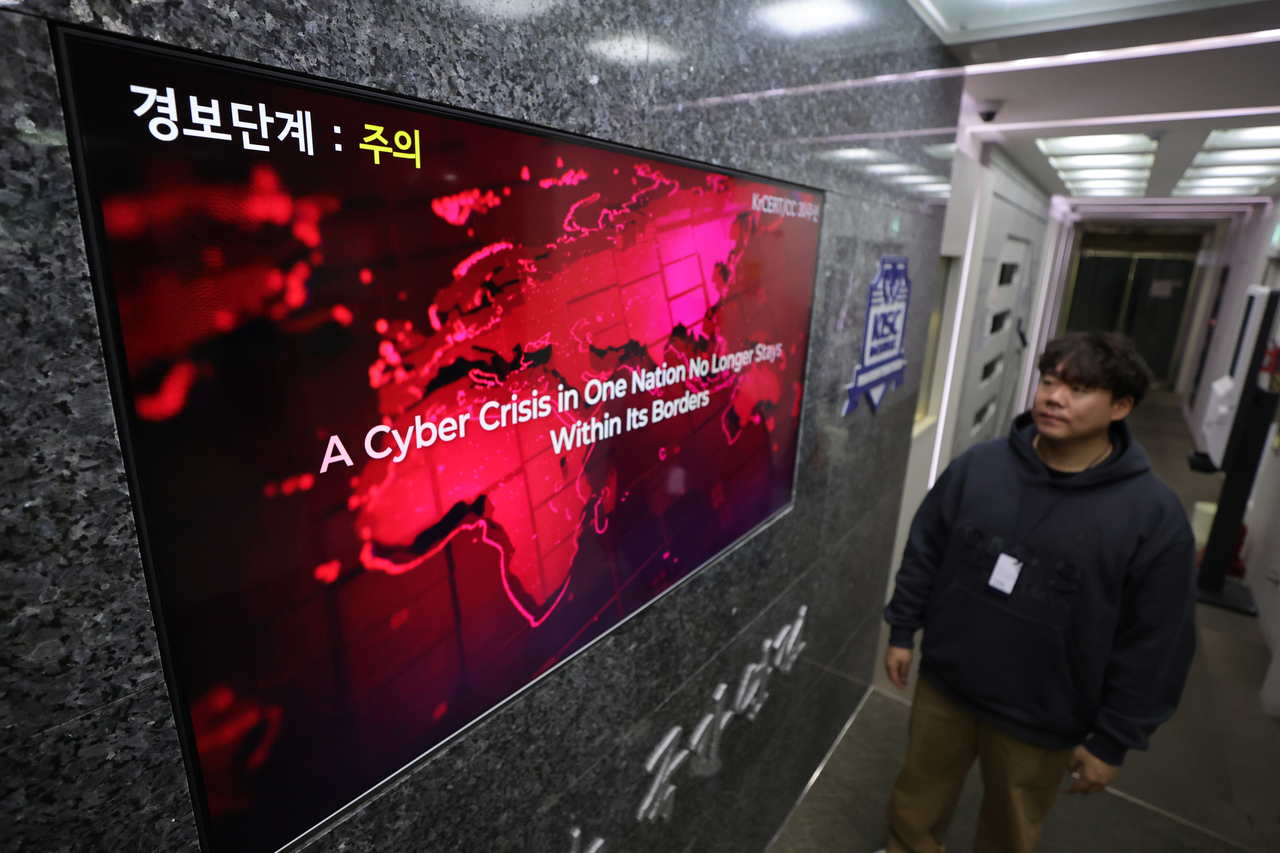
The latest discovery follows the uncovering of serious vulnerabilities in PHP, a programming language used for websites, which prompted South Korea to raise its private-sector cybersecurity alert level from "interest" to "caution" on Oct. 22.
yeeun@heraldcorp.com